Company
Security, trust, and the accuracy SLA
What the 99.5% figure measures, how a record is verified, where your data lives, and exactly where our certifications stand today.
Verified field accuracy
Jurisdictions
Architecture
Source to output, with nothing hidden in between.
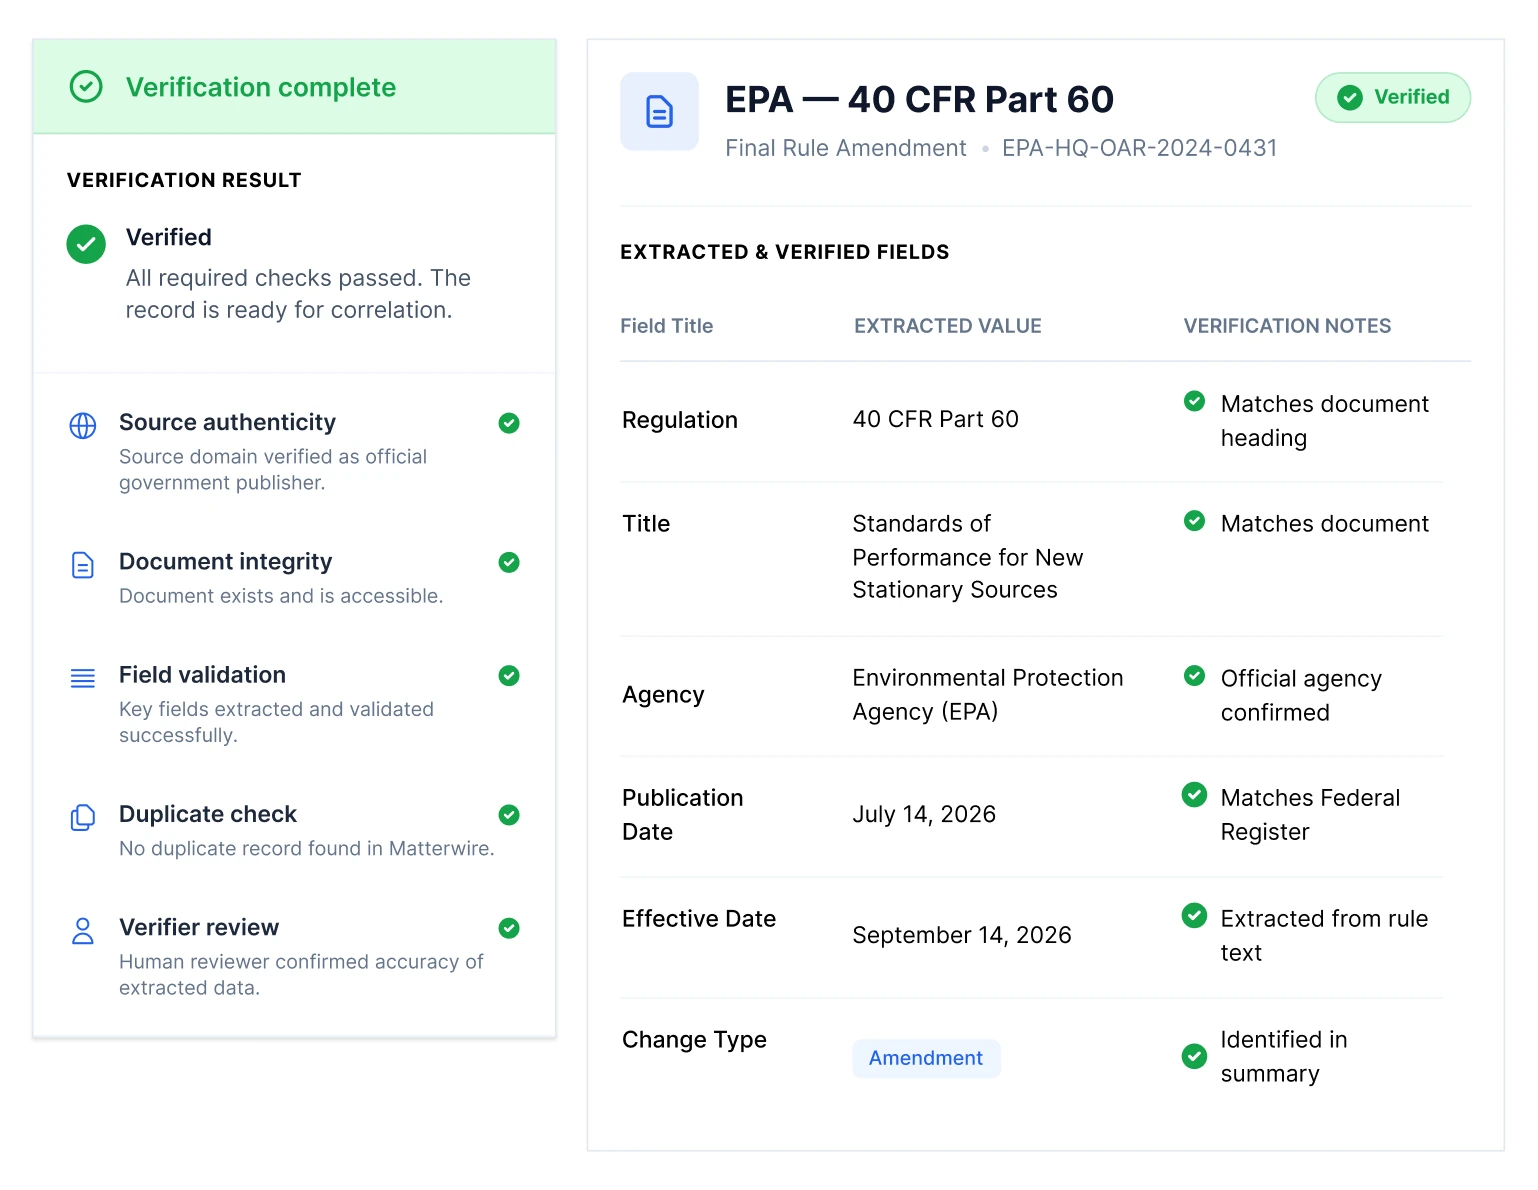
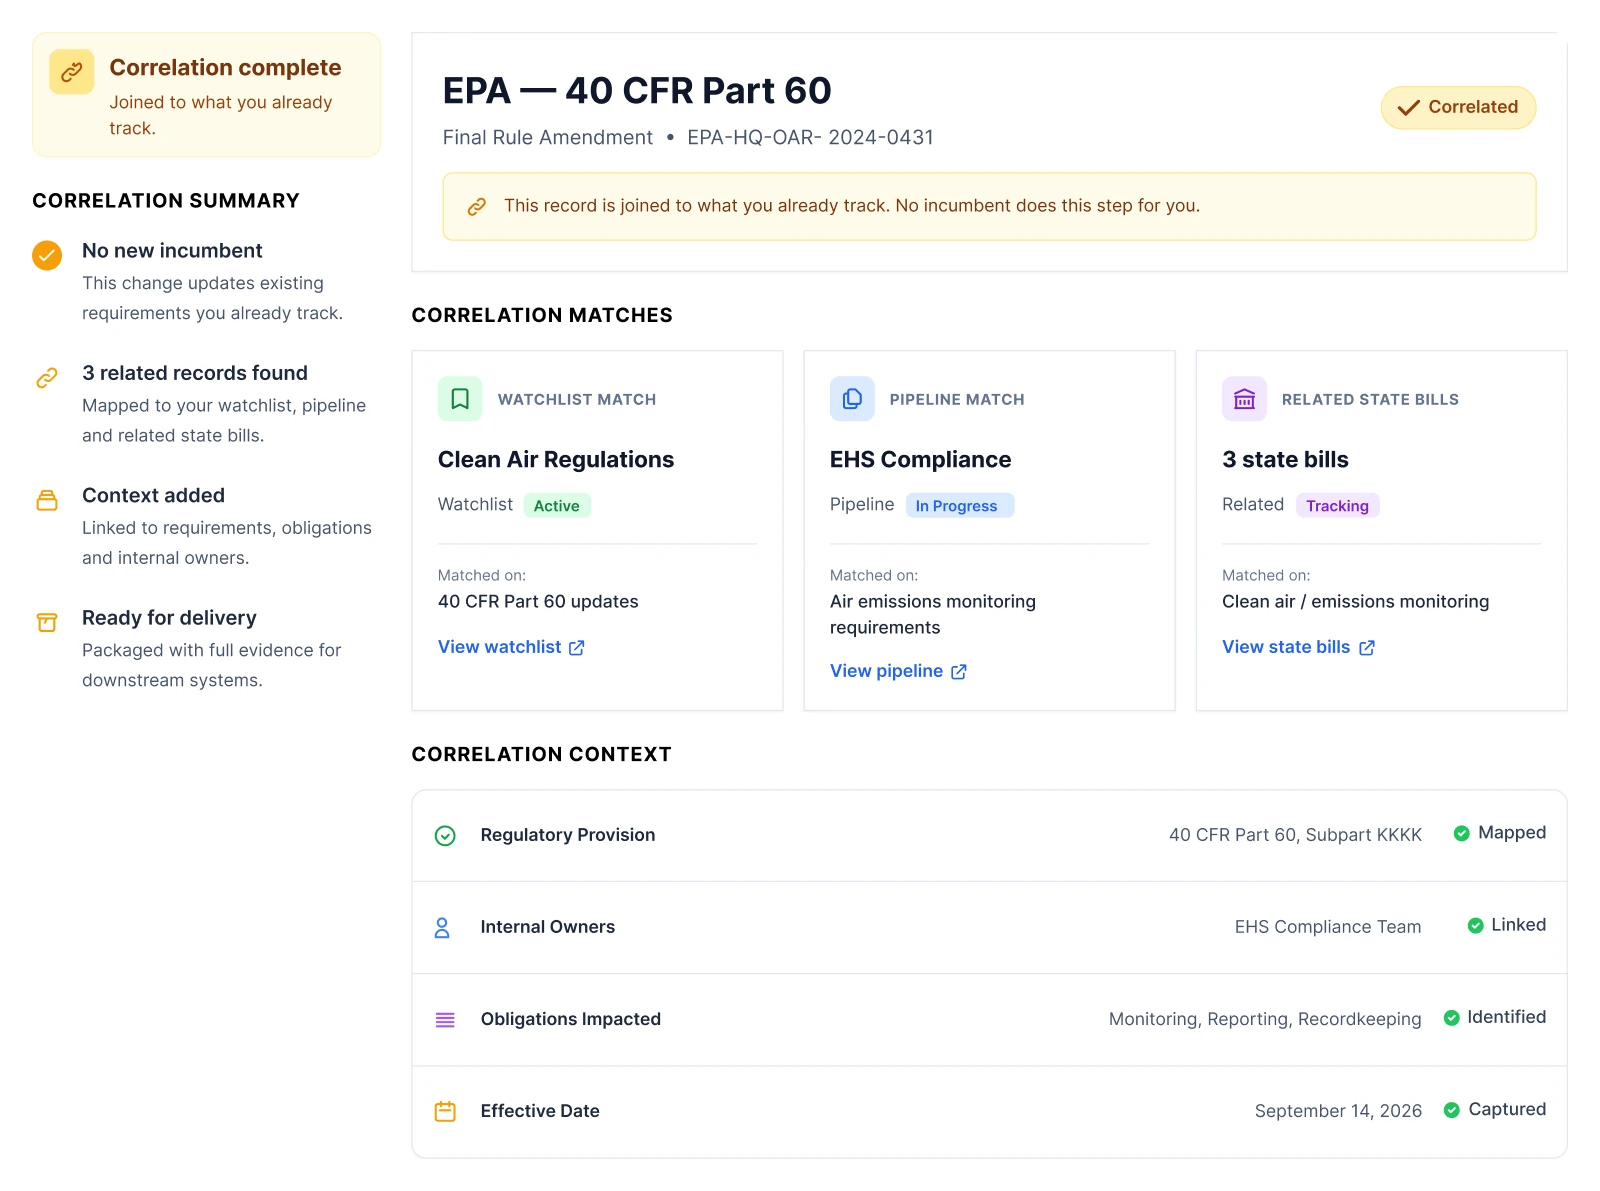
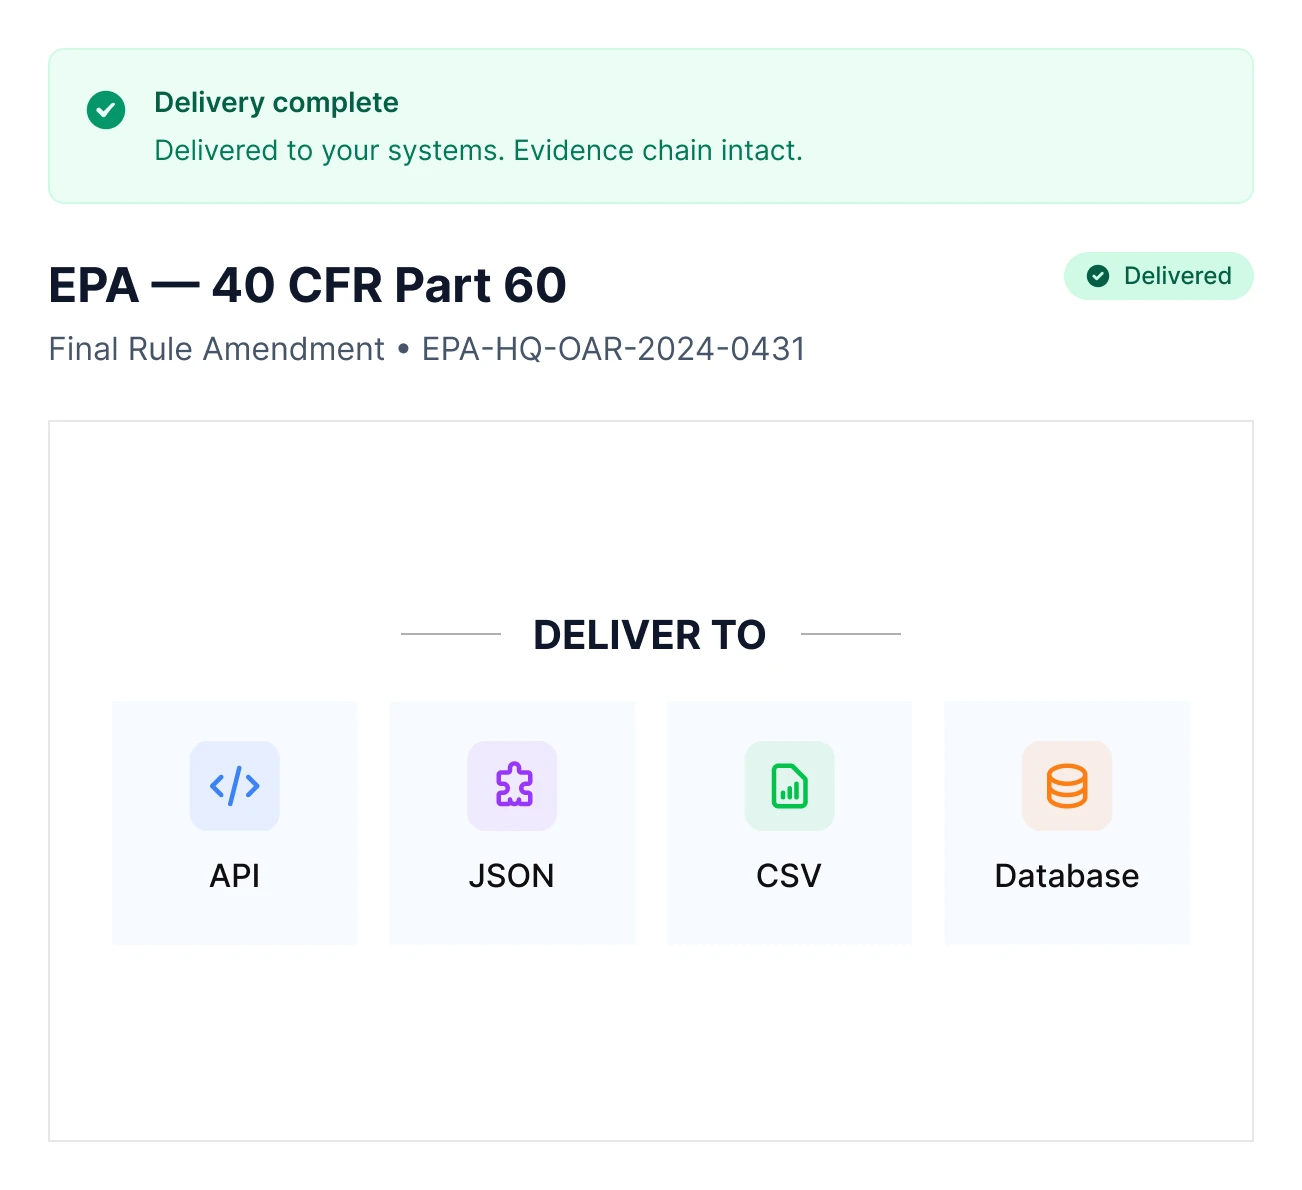
Six stages. The two shaded ones are where Matterwire differs from a monitoring feed: verification happens before release, and correlation happens before delivery.
01
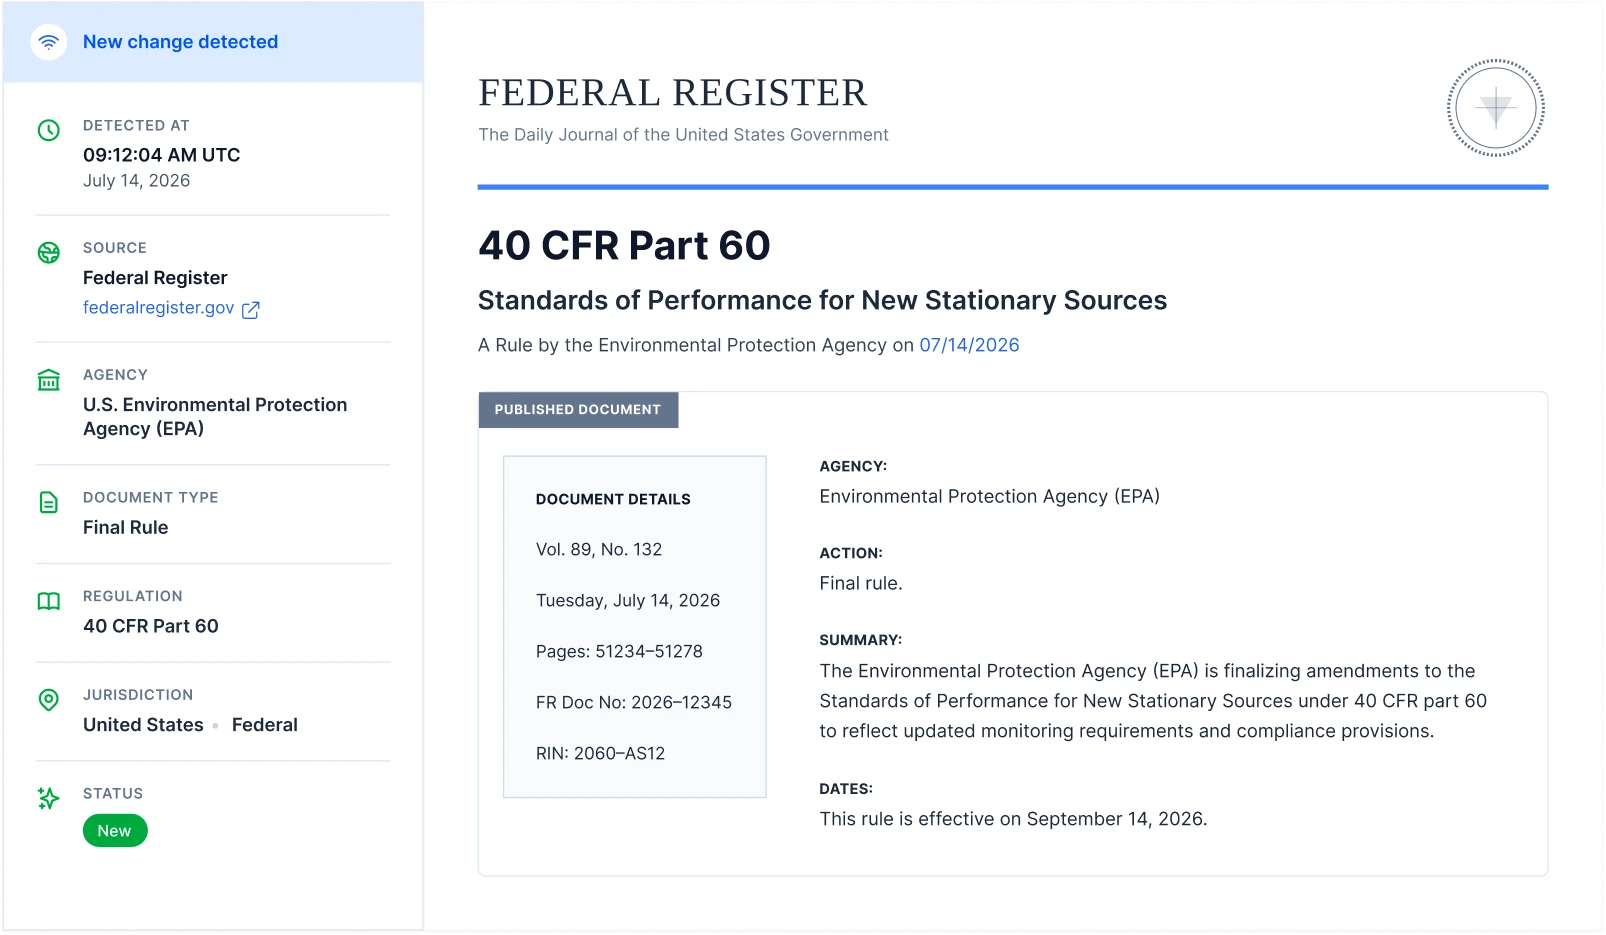
Detected
The Federal Register entry, captured at 09:12 with its source URL. This is where most trackers stop.
What we hold, and where.
Hosting
AWS. Regulatory source documents are public records. Customer configuration and delivery targets are encrypted in transit and at rest.
What we store about you
Your watchlists, your delivery targets and your users. We do not hold your CRM records or your warehouse contents; we write into them.
Model training
Customer data is never used as training data. Extraction runs against public regulatory source documents.
Access control
Scoped API tokens, signed webhooks, and role-based access with SSO on Enterprise. Access to the evidence store is itself logged.
Why provenance is a privacy control.
Under GDPR Article 83(5), the most serious infringements are subject to administrative fines up to
Lower-tier procedural breaches under Article 83(4) cap at €10,000,000 or 2%.
Regulators ask for provenance
A regulator asking how a control was arrived at is asking a provenance question. Per-record source URLs, capture timestamps and verifier IDs answer it directly. That is the case for building the audit trail into the monitoring rather than bolting it on.
Matterwire is GDPR-aligned
Our processing terms, subprocessor list and data-subject request process are available on request, and the privacy policy sets out what we collect and why.
Why provenance is a privacy control.
GDPR alignment
Processing terms, subprocessor list and DSR process available on request.
AWS hosting, encryption in transit and at rest
TLS enforced on all endpoints. Secrets held in a managed vault.
SOC 2 Type II
Readiness work underway. Report and audit period will be published when the audit completes.
ISO 27001
On the roadmap after SOC 2. No certification is claimed today.
Security questions that need a specific answer go to security@matterwire.io.
Questions
What procurement asks first.
Correctness at the field level across a sampled population of published records, not correctness at the document level. A record with a correct title and a wrong effective date counts as one field error, not as a correct record.
Bring your security questionnaire.
Book a demo and we will work through it on the call, including the accuracy methodology and the retention configuration.
No obligation. We will use your own jurisdictions in the call.